HTTP/3 changes how a browser carries web requests to a server. It uses QUIC over UDP, allowing separate streams to make progress without the TCP connection-wide blocking that can affect HTTP/2 when packets are lost. That can help some visitors on less reliable networks, but switching the protocol does not guarantee a faster website. Your application, assets, cache and network path still matter.
The practical work is to identify where HTTPS terminates, enable HTTP/3 there, keep a working fallback and verify an actual HTTP/3 connection. A cPanel account, an unmanaged Nginx VPS and a proxied CDN hostname need different changes. This guide follows each route and shows how to tell a successful negotiation from an advertised feature.
Check the HTTP/3 Prerequisites
Start with the hostname visitors use. If it points through a CDN, the browser connects to the CDN edge; the CDN then makes a separate request to your origin. Enabling HTTP/3 on either side says nothing by itself about the other connection. The HTTP/3 specification explains the protocol; the deployment decision starts with your own connection path.
| Requirement | What to check | Why it matters |
|---|---|---|
| Working HTTPS | The public hostname has a valid certificate and loads normally. | Resolve certificate and hostname errors before adding another transport. |
| HTTP/3 support | The server or CDN supports QUIC and HTTP/3 on the chosen endpoint. | A panel label or a recent package version alone does not prove the feature is active. |
| UDP reachability | UDP port 443 is allowed through the host firewall and any upstream firewall or load balancer. | An HTTPS rule for TCP does not automatically admit QUIC traffic. |
| TCP fallback | HTTPS over TCP still works. | Some clients and networks cannot use QUIC. |
| A capable test client | The browser supports HTTP/3, or the curl build lists HTTP3. | An unsupported client cannot validate your server configuration. |
Back up the configuration you will change and choose one test hostname first. On managed hosting, ask which web server handles the public HTTPS connection and who controls its listeners and firewall. Our managed VPS and cPanel guide can help you separate account-level work from server administration.
Use the Supported cPanel or Plesk Route
On cPanel, identify the web server first. HTTP/3 is not enabled by the Optimize Website compression screen. cPanel documents that screen as a compression control. If the server uses LiteSpeed, follow its cPanel integration; if your provider uses another front end, ask for that stack’s supported procedure. Do not replace panel-managed configuration files with a generic Nginx example.
On Plesk for Linux, HTTP/3 support remains experimental. With the required nginx component installed, Plesk’s documented server-wide command enables it for websites across the server. Run it only if you administer that server and intend that scope:
plesk bin http3_pref --enable -nginx
Confirm the operating system is supported and allow UDP port 443. Website-level control is available under Websites & Domains → Hosting & DNS → Apache & nginx → HTTP/3 support. Use the current Plesk HTTP/3 instructions for prerequisites and your installed version.
As checked on 21 September 2026, Plesk also documents an intermittent packet-size failure affecting some connections. Review that issue in the troubleshooting section before a broad rollout, particularly if testing succeeds on one network but fails on another.
Configure Nginx on an Unmanaged VPS
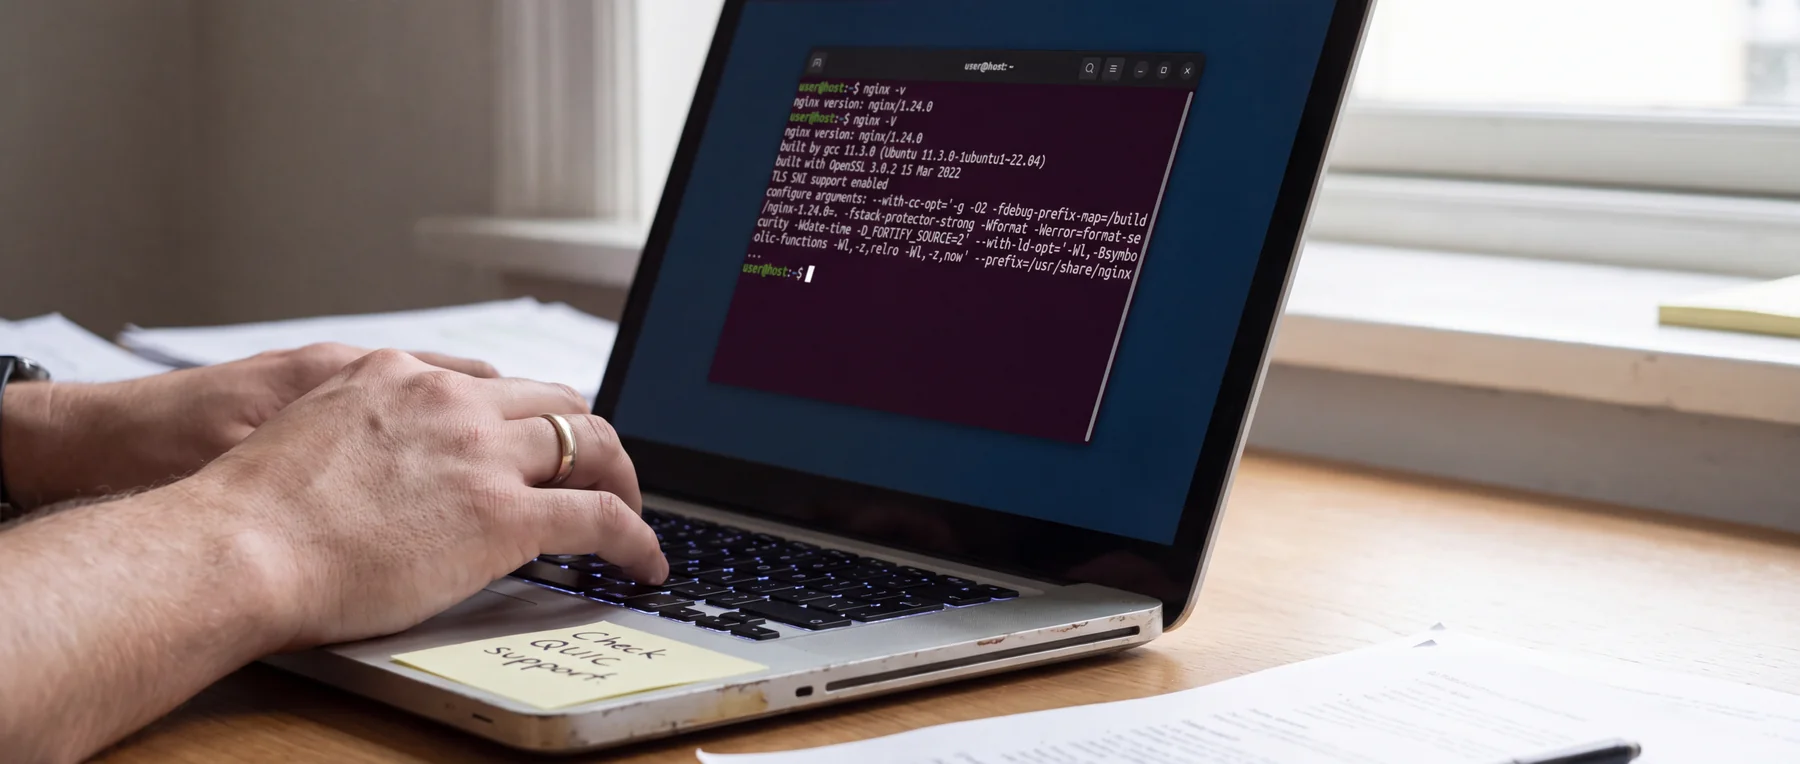
Use a maintained, patched Nginx package appropriate for your operating system. Review the official package instructions and QUIC build requirements rather than installing an old release just because it introduced HTTP/3. Inspect the installed binary:
nginx -V
Check its configure arguments for –with-http_v3_module. The example below also uses the HTTP/2 module and the separate http2 directive, which requires Nginx 1.25.1 or later. See the HTTP/3 module reference and HTTP/2 reference for the supported syntax.
This is a small static test site inside the existing HTTP configuration. Replace the hostname and certificate paths, and create a separate directory containing only a test HTML file. It is not a complete WordPress, PHP or panel configuration. Preserve your application’s existing routing, security headers and access controls when adapting the listener settings later.
server {
    listen 443 ssl;
    listen 443 quic reuseport;
    http2 on;

    server_name example.com;
    ssl_certificate /etc/letsencrypt/live/example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem;
    ssl_protocols TLSv1.2 TLSv1.3;

    root /var/www/http3-test;
    index index.html;
    add_header Alt-Svc 'h3=":443"; ma=86400' always;

    location / {
        try_files $uri $uri/ =404;
    }
}
The two listeners keep TCP HTTPS available alongside QUIC. The Alt-Svc response header advertises HTTP/3; it does not prove that a client used it. On servers with several virtual hosts sharing an address and port, check the existing listener configuration before adding reuseport again. Add corresponding IPv6 listeners only when IPv6 is configured and reachable.
After checking the firewall and certificate paths, test the configuration. On a systemd installation with the standard service name, reload only if the test passes:
sudo nginx -t && sudo systemctl reload nginx
Then test from another network. A successful local reload confirms configuration syntax, not external UDP reachability or browser negotiation.
Check LiteSpeed and OpenLiteSpeed Settings
For LiteSpeed Web Server with cPanel, the official QUIC and HTTP/3 guide describes support for Apache HTTPS virtual hosts and the required UDP access. Verify the certificate and the actual web-server configuration even when the feature is enabled by default.
For OpenLiteSpeed or a standalone installation, check the installed edition’s WebAdmin controls at the server, secure listener and virtual-host levels. The relevant settings include HTTP/3 or QUIC enablement and opening the listener’s UDP port. A virtual-host setting can still prevent the site from using the feature. Consult the server tuning reference and virtual-host SSL reference; do not copy settings from a different edition without checking them.
HTTP/3 does not replace ordinary page optimization. Continue to reduce unnecessary requests and oversized assets; our cPanel loading-speed checklist covers complementary work.
Enable HTTP/3 at the CDN Edge
A CDN can provide HTTP/3 to visitors without requiring HTTP/3 at your origin. In Cloudflare, open the selected zone’s Speed → Settings → Protocol Optimization settings and enable HTTP/3. Verify that the hostname is proxied and that edge HTTPS works.
Cloudflare’s documentation explicitly distinguishes the visitor-to-edge connection from the origin connection: HTTP/3 to origins is not supported in the documented setup as checked on 21 September 2026. Seeing HTTP/3 in a browser therefore does not establish that your VPS negotiated HTTP/3. Keep origin HTTPS configured and test each endpoint for its own purpose.
For another CDN, follow its current zone or distribution instructions. Check certificate activation and hostname routing before treating the control-panel switch as completion.
Verify the Negotiated Protocol
In browser developer tools, open the Network panel, display the Protocol column and reload the page. An entry showing h3 is evidence for that request. A first request may use HTTP/2 while the browser discovers HTTP/3, and different resources may use different hosts.
For a repeatable command-line check, first inspect your curl build:
curl -V
Its feature list must include HTTP3. Then replace the example hostname and run this bounded test:
curl --http3-only \
  --connect-timeout 10 --max-time 30 \
  --silent --show-error --output /dev/null \
  --write-out 'HTTP version: %{http_version}\n' \
  https://example.com/
Check both the reported protocol and whether curl exits successfully. The curl HTTP/3 documentation distinguishes –http3-only, which requires HTTP/3, from –http3, which permits a fallback. A successful fallback is useful for visitors but is not proof of a working HTTP/3 endpoint.
The command tests the hostname’s public endpoint, including a CDN if one is in front. It checks transport negotiation, not whether the page content is correct: a server can return an HTTP error over a successful HTTP/3 connection. Inspect the page and its response status separately.
Troubleshoot Fallback and Connection Failures
| Observation | Likely check | Next action |
|---|---|---|
| The page works, but requests use HTTP/2. | Client support, discovery or fallback. | Check the request hostname and retry with an HTTP/3-capable client using the strict curl test. |
| The strict test times out. | UDP listener and the complete network path. | Check host and upstream firewall rules, then compare a second external network. |
| The CDN uses HTTP/3, but the origin does not. | Separate connections. | Confirm the CDN’s origin-protocol support before changing the VPS. |
| Only some Plesk connections fail with a packet-size error. | The documented Plesk issue and affected version. | Review the vendor workaround and retain working HTTPS fallback. |
Plesk’s 15 September 2026 support notice tracks issue PPPM-15525, including sendmsg() failed (90: Message too long) in logs. At the review date, the vendor described a future fix and an HTTP/3-disable workaround. Use the documented website-level control where available if that issue affects your deployment; retest ordinary HTTPS after the change.
For any stack, record the client version, hostname, network, time and error before changing settings. That makes it easier to separate a server problem from a particular mobile carrier, VPN or local firewall.
Roll Out HTTP/3 With a Measurable Goal
Choose a small set of representative pages and compare the same content, cache conditions, geography and device classes before and after the change. Watch page-loading experience and errors as well as protocol adoption. Include mobile and higher-latency connections, where transport behavior may differ from an office connection.
Keep the change if it produces a useful result for your visitors without increasing failures. If it does not, investigate the application and network bottlenecks rather than promising a fixed percentage speed gain. Keep TCP HTTPS available throughout the rollout.
If you want control over the web-server build and configuration, explore HostStage’s unmanaged Linux VPS options. Choose a supported stack you can maintain, then validate the exact hostname and network path before making HTTP/3 part of your deployment.
FAQ
Does HTTP/3 automatically make a website faster?
No. It can help particular network conditions, but the result depends on the client, connection and workload. Measure your own pages instead of assuming a universal improvement.
Can I enable HTTP/3 from a normal cPanel account?
That depends on the hosting stack and permissions. The Optimize Website screen controls compression. Ask the server administrator which component terminates HTTPS and whether HTTP/3 is supported there.
Do I need to open TCP and UDP port 443?
A direct web-server deployment normally needs UDP 443 for QUIC and TCP 443 for HTTPS fallback. Review every firewall or load balancer on the path, not just the operating system.
Does an Alt-Svc header prove HTTP/3 is working?
No. It advertises availability. Confirm an actual request through the browser’s protocol column or an HTTP/3-only client test.
Must my origin support HTTP/3 when I use a CDN?
Not necessarily. The browser-to-CDN and CDN-to-origin connections are independent. Check the CDN’s documented origin support and verify each connection separately.